

Security leaders worry AI agents outpace governance
Tue, 29th Sep 2026 (Today)
Zentera Systems has released a survey-based report on AI agent security governance, finding widespread concern among security leaders about their ability to control and monitor the technology.
The report, titled Agents of Change, is based on responses from 251 security leaders surveyed with research agency TrendCandy. It highlights a gap between the pace of AI agent deployment in organisations and the controls used to govern access, oversight and accountability.
One of the main findings is the scale of current deployments. According to the survey, 58 per cent of organisations already operate more than 50 AI agents. Within the next 12 months, 66 per cent expect to run more than 50 agents, while 38 per cent expect to have more than 100 in use.
The data also suggests AI adoption is being driven from the top of organisations. Thirty-six per cent of respondents strongly agreed that company leadership had directed the deployment of AI agents or agentic tools.
Context risks
Respondents were more concerned about where and under what authority agents act than whether they can complete a task. Seventy-five per cent said they were concerned that an AI agent could perform the right task in the wrong environment or location.
A further 84 per cent said agents can cross project boundaries more easily than employees, while 80 per cent were concerned that agents may have access that was never explicitly granted. The report argues that a technically correct action can still be unauthorised if it takes place in the wrong setting or reaches the wrong data or systems.
When asked what would be needed before expanding deployments further, security leaders ranked authorisation controls above other measures. Explicit authorisation ranked first at 56 per cent, followed by project isolation at 51 per cent and session logging at 48 per cent.
Project-level isolation was seen as particularly important. Eighty-five per cent of respondents said it was essential or very essential for AI adoption, while 87 per cent agreed that authorisation is the missing layer in agentic AI security.
Confidence gap
High-confidence oversight remains limited. Only 43 per cent of leaders said they were very confident they could demonstrate what AI agents were explicitly authorised to do.
Confidence fell further on other measures. Thirty-eight per cent said they were very confident they could prove what an agent did through audit records, and 37 per cent said they monitor agent activity very closely.
That matters because many respondents expect their organisations to tighten controls after initial rollouts. The study found that 79 per cent expect their organisation will need to claw back or significantly restrict AI agent usage within the next 18 months.
The report points to a broader market expectation that some current deployments will be scaled back if governance issues are not addressed after systems enter production. That aligns with concerns among security teams that enthusiasm for AI agents is outpacing the operational controls needed to supervise them.
Respondents came from a range of sectors, although the sample leaned heavily towards technology-related industries. Semiconductors accounted for 70 per cent of the sample, followed by software and SaaS at 51 per cent and financial services at 43 per cent. Pharmaceutical and life sciences organisations made up 14 per cent.
Zentera used the findings to argue for stronger boundaries around AI agents, including identity-based access decisions, project separation and better audit trails. It also linked the study to its own product, Ensage AI, which the company said is designed to address gaps in discovery, authorisation, containment, observation and maintenance of AI agents.
The findings come as companies across industries test autonomous and semi-autonomous software agents for internal workflows, customer support, software development and business operations. Those deployments have expanded the security debate beyond model safety to include practical questions such as who authorised an action, what systems an agent could reach and whether teams can reconstruct activity after the event.
In that context, the data suggests many security leaders believe current governance methods are not keeping pace with the growth of agent-based systems. The issue is not only whether AI agents can act, but whether organisations can show those actions were permitted, bounded and visible when they occurred.
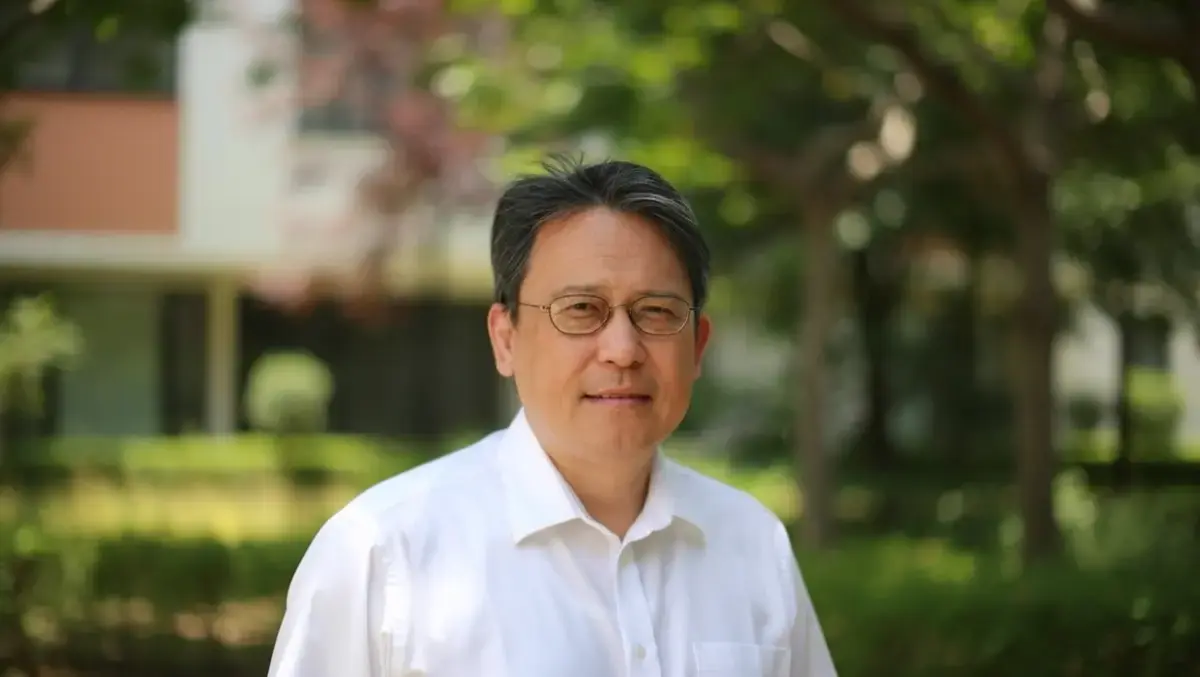
"With the rapid growth of AI agents within organizations, cybersecurity methods have not evolved quickly enough to keep up," said Dr. Jaushin Lee, Chief Executive Officer of Zentera Systems.
"We discovered that security leaders are seeing AI use continuing to expand but lack confidence in their ability to effectively monitor and secure that technology. The study reveals that they require, but are in most cases lacking, a stricter governance model that closely monitors AI agents while also restricting their permissions, actions, and network access," Lee said.