

SEON has expanded its Signal Intelligence platform to more than 1,100 proprietary data points, extending coverage across address intelligence, session behaviour, phone and carrier data, digital footprint information, and device signals.
The Austin-based fraud prevention and anti-money laundering software provider said the changes are intended to help risk teams identify inconsistencies in customer identities and detect links between accounts that may be part of wider fraud rings.
The expansion comes as financial crime teams grow increasingly concerned about the use of generative artificial intelligence in identity fraud. SEON cited findings from the Financial Action Task Force that deepfakes can now be created rapidly on consumer devices, while ACAMS has reported that 75% of anti-financial crime professionals have ranked misuse of generative AI as their top emerging risk for the third year in a row.
For fraud investigators, the challenge is that individual data points can appear legitimate in isolation. A device may seem normal, an address may validate correctly, and an email may pass standard checks, but mismatches between those signals can reveal that an identity has been fabricated or reused.
Broader coverage
SEON said the expanded dataset is designed to give fraud teams more independent sources of evidence across three areas: identity history, shared infrastructure, and live behaviour.
For digital footprint checks, coverage now includes AI developer platforms, job boards, real estate websites, and dating applications, allowing investigators to see where an email address or phone number has appeared over time. The company has also added phone intelligence data on SIM-swap and number-porting history.
For address intelligence, SEON now verifies and standardises addresses across more than 240 countries and assigns identifiers to specific addresses and buildings. This is intended to help teams spot cases in which multiple supposedly unrelated accounts cycle through variations of the same location, such as different unit numbers or formatting changes.
Device-related additions include signals designed to detect AI-agent activity, compromised iOS devices, Android eSIM mismatches, and discrepancies between network country data and a visible IP address that may be obscured by a virtual private network.
The expansion also adds session monitoring across customer onboarding, login, account recovery, checkout, and payment. This can help teams detect automation, remote access, off-screen activity, and active calls during a live session before suspicious behaviour develops into an account takeover.
Shared evidence
The new data points can be used within the platform for rules, alerts, customer reviews, and network investigations. They can also be connected to external investigator AI tools through SEON's Model Context Protocol server, allowing human analysts and software agents to work from the same evidence base.
According to the company, this is intended to reduce the gap between initial detection and later investigation by carrying the same supporting information through each stage of a case.
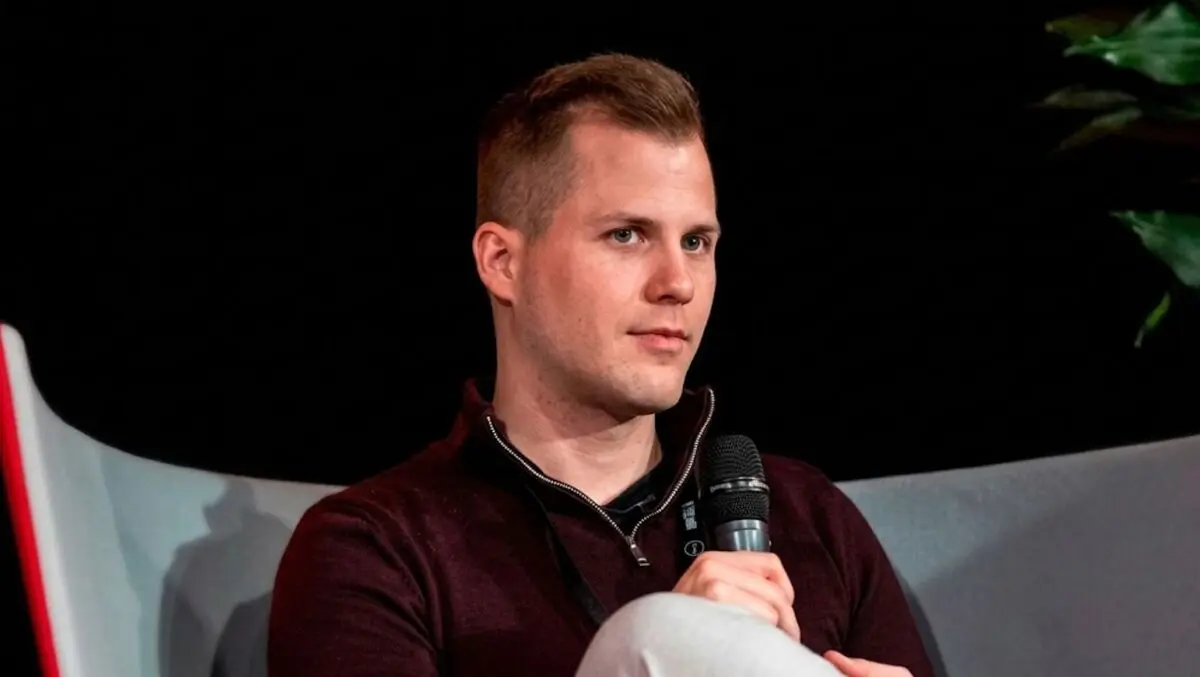
Tamas Kadar, Chief Executive Officer and Co-Founder of SEON, said the broader set of signals is intended to make it harder for criminals to hide synthetic or manipulated identities.
"AI has made a believable identity cheap to produce. What fraudsters cannot easily do at scale is build a consistent history for every account without reusing infrastructure," said Tamas Kadar, Chief Executive Officer and Co-Founder of SEON. "That is where our signal foundation makes the difference. The more dimensions a fraud team can check simultaneously, the harder it is to hide an identity that does not add up."
Alongside the product expansion, SEON has introduced Hidden Risk Files, a series of short investigations written by the company's fraud consultants. The series follows individual suspicious clues through to wider fraud networks and is intended to show how specific signals can reveal broader patterns.
The first case focuses on how a screen-brightness reading was used to connect thousands of accounts in a fraud ring operating across Android hardware.