

New Zealand cyber agency warns firms to patch PHP flaws
Mon, 9th Nov 2026 (Today)
New Zealand's National Cyber Security Centre has urged businesses to check whether recently disclosed PHP vulnerabilities affect their websites and online services.
It says businesses should act immediately to find out whether PHP is used in their systems and to ensure security updates have been applied. Organisations unsure whether their sites or services rely on PHP should speak to their website developer, IT provider or hosting company.
PHP is a coding language used across many websites and web-based services. The NCSC warned the vulnerability could allow an attacker to take full control of a website, web server or web service, leading to risks including website defacement and outages.
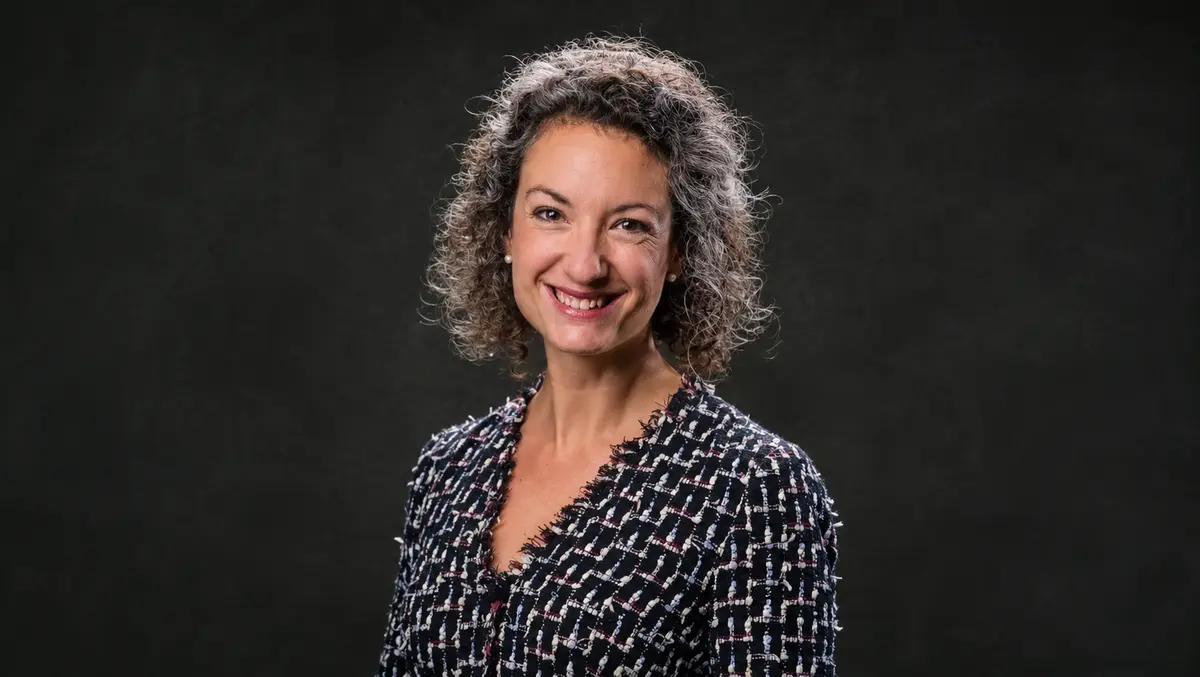
"If you're not sure whether your website uses PHP, the first step is to contact your website developer, IT provider or hosting company. They can tell you whether your website or services could be affected and whether the latest security updates have been applied," said Dr Emma Bickerstaffe, Director of Cyber Defence Operations at the National Cyber Security Centre.
The issue could affect businesses using content management systems such as WordPress that rely on PHP. Organisations may also be exposed if their websites or online services are hosted by third-party providers using PHP, or if they run web applications that depend on the language.
For many businesses, that means the task extends beyond internal technology teams. Companies that outsource web development or infrastructure may need confirmation from suppliers that updates have been applied and checks for signs of compromise have been completed.
"This vulnerability could be used by an attacker to take full control of a website, web server or web service, and could include defacing or taking down websites. All systems using PHP need to patch the software," Bickerstaffe said.
What businesses should ask
The agency set out a series of questions businesses should raise with service providers if they are unsure about their exposure. These include whether the latest PHP security update has been installed, whether any systems are affected by the vulnerability, whether checks were carried out to identify compromise before patching, and whether any further action is needed to secure affected systems.
Organisations that cannot apply updates straight away should also ask what temporary measures are being used to reduce risk. That reflects a common problem in cyber incident response, where immediate patching is not always possible because of operational constraints, third-party dependencies or compatibility concerns.
"If you are unsure, businesses should ask their website developer, IT provider or hosting company whether the latest PHP security update has been applied. You can also ask whether any systems are affected by the vulnerability, whether checks have been undertaken to identify any compromise prior to patching, and whether any additional actions are required to secure their systems," Bickerstaffe said.
Checks after patching
Applying an update should not be treated as the final step. The NCSC urged providers to look for signs that systems may already have been accessed or altered before a patch was installed.
Warning signs include unexpected changes to websites, the creation of new administrator accounts, outages, poor performance, and unusual login or system activity. These checks are intended to help businesses determine whether an attacker exploited the flaw before remedial action was taken.
"Businesses should not assume that applying an update is the end of the process," said Dr Bickerstaffe. "Providers should also be checking for signs of unusual activity, including unexpected changes to websites, the creation of new administrator accounts, outages or poor performance, and unusual login or system activity."
Advice for users
The warning was directed at businesses and service providers rather than the general public. Internet users do not need to take action simply because they have visited a website that uses PHP, the NCSC said.
"This vulnerability affects the systems delivering website content or services," said Dr Bickerstaffe. "People browsing the internet do not need to take action, and visiting a website that uses PHP does not place phones or home computers at risk."
The agency said it was still too early to judge the full impact of the vulnerabilities on organisations in New Zealand. "At this point the priority for businesses is to confirm whether they are affected and ensure appropriate security updates and checks have been completed as a priority," Bickerstaffe said.